

The most common method to compromise a system security is to exploit it by creating a payload that gives you a reverse shell. A great tool for creating payloads is FatRat. FatRat is a powerful exploitation tool that can bypass most of the antivirus ...
Read More

Shellter is a dynamic shellcode injection tool used to inject payloads into a Windows executable (EXE) file. This injection allows you to disguise a payload or malicious code into a real executable file. In order to demonstrate this technique, I am ...
Read More

In this article, I will show you gain control over the target browser using the BeEF framework and a basic captive portal page. BeEF works by using a JavaScript file named hook.js. The job of the attacker is to find a way to run this JavaScript on t...
Read More
The word BeEF stands for Browser Exploitation Framework. The tool was designed to explore the vulnerabilities in browsers and test them. BeEF hacking involves hooking one or more web browsers and using them to launch command modules to attack the ta...
Read More
In this article, you will learn how to get gain full control over the target machine using the BeEF framework and Shellter. So, first off you need to inject the malicious code or reverse TCP meterpreter payload into a real executable file. To do tha...
Read More

In this article, I will show you how to steal login credentials from an enterprise wireless network. For those who don’t know there are two versions of WPA, personal and enterprise. Both use a strong encryption method called AES-CCMP to encrypt data...
Read More
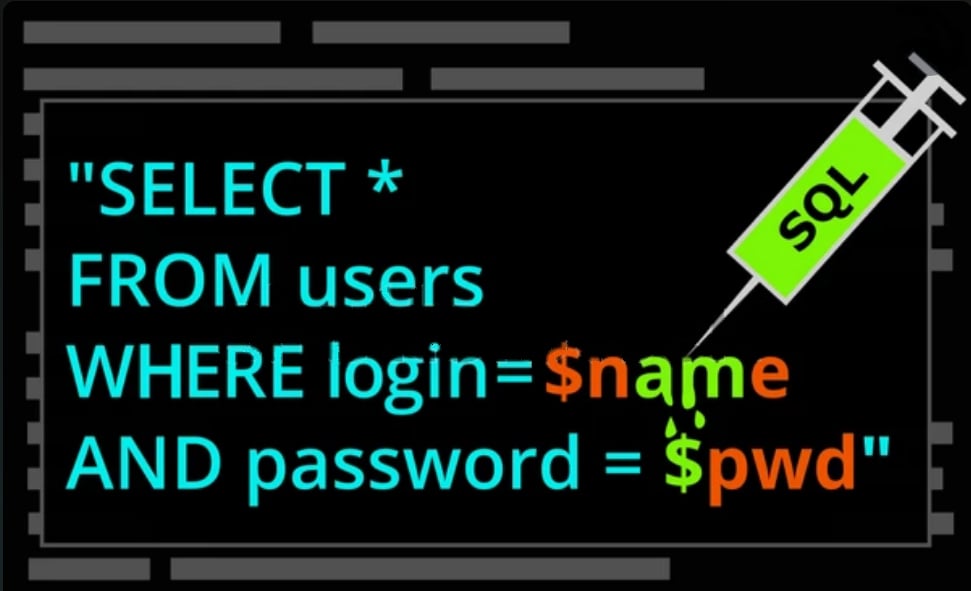
SQL Injection is a web hacking technique of inserting SQL commands in user-supplied data fields of web applications and submitting them for execution by the database server. To perform a SQL injection attack, an attacker inserts malicious SQL code, ...
Read More
In this tutorial, you’re going to learn how to reset/remove forgotten passwords on any Windows computer. Using this method you can unlock any Windows device without knowing the user password and without formatting the hard disk. To perform this expe...
Read More
In this guide, you’ll learn how to password protect a directory on your website by implementing a username/password authentication using nginx HTTP basic auth.HTTP basic authentication allows you to stop other people who don’t have the login credenti...
Read More
In this tutorial, you will learn how to find someone’s location by using a tool called Seeker. The great thing about Seeker is that other tools and services provide IP geolocation, which is NOT accurate at all and only provides an ISP location rathe...
Read More
In this article, I will show you how to detect wireless deauthentication attacks on your network. Due to weaknesses in the way Wi-Fi works, it’s extremely easy to disrupt most Wi-Fi networks using tools that forge deauthentication packets. Most comm...
Read More
In this article, I will show you how to control an Android phone from your Linux desktop computer using an application called “scrcpy”.Scrcpy is a free, open-source tool that allows you to display and control an Android phone/device from your compute...
Read More
In this tutorial, I’ll show you how to encrypt and decrypt files with GPG.GPG is a security tool for encrypting files like emails, messages, or just anything you need to send to someone securely.Install GPGGPG can be found in most Linux distributions...
Read More
A captive portal is a customized login page that is displayed to newly connected users of a Wi-Fi network before they are granted access to the network. Captive portals are often used in public places, such as airports, hotels, schools, and other pl...
Read More

Cross-Site Scripting is a web-based attack performed on vulnerable web applications where an attacker can create a malicious link to inject unwanted executable JavaScript into a website. A Cross-Site Scripting attack involves executing malicious cod...
Read More